


Journal of Computer Applications ›› 2026, Vol. 46 ›› Issue (9): 2877-2888.DOI: 10.11772/j.issn.1001-9081.2025081026
• Cyber security • Previous Articles
Kan HE1,2( ), Hongfeng MA1,2, Xuejun ZONG1,2, Hongyan SHI1,2, Lian LIAN1,2, Bowei NING2,3
Received:2025-09-08
Revised:2025-10-10
Accepted:2025-10-27
Online:2025-11-07
Published:2026-09-10
Contact:
Kan HE
About author:HE Kan, born in 1978, M. S., associate professor. His research interests include industrial information security.Supported by:
何戡1,2(), 马洪峰1,2, 宗学军1,2, 史洪岩1,2, 连莲1,2, 宁博伟2,3
通讯作者:
何戡
作者简介:何戡(1978—),男,辽宁沈阳人,副教授,硕士,主要研究方向:工业信息安全基金资助:CLC Number:
Kan HE, Hongfeng MA, Xuejun ZONG, Hongyan SHI, Lian LIAN, Bowei NING. DCSFFuzzer: dual-channel semantic feature fusion-based fuzz testing method for industrial control protocols[J]. Journal of Computer Applications, 2026, 46(9): 2877-2888.
何戡, 马洪峰, 宗学军, 史洪岩, 连莲, 宁博伟. 融合双通道语义特征的工业控制协议模糊测试方法DCSFFuzzer[J]. 《计算机应用》唯一官方网站, 2026, 46(9): 2877-2888.
Add to citation manager EndNote|Ris|BibTeX
URL: https://www.joca.cn/EN/10.11772/j.issn.1001-9081.2025081026
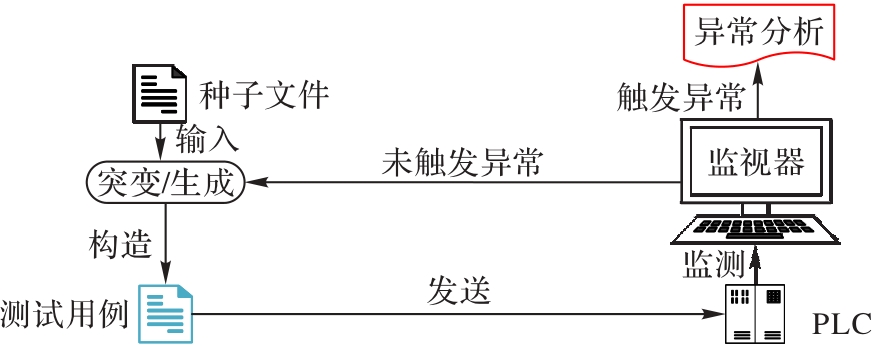
Fig. 1 Flow of fuzzy testing
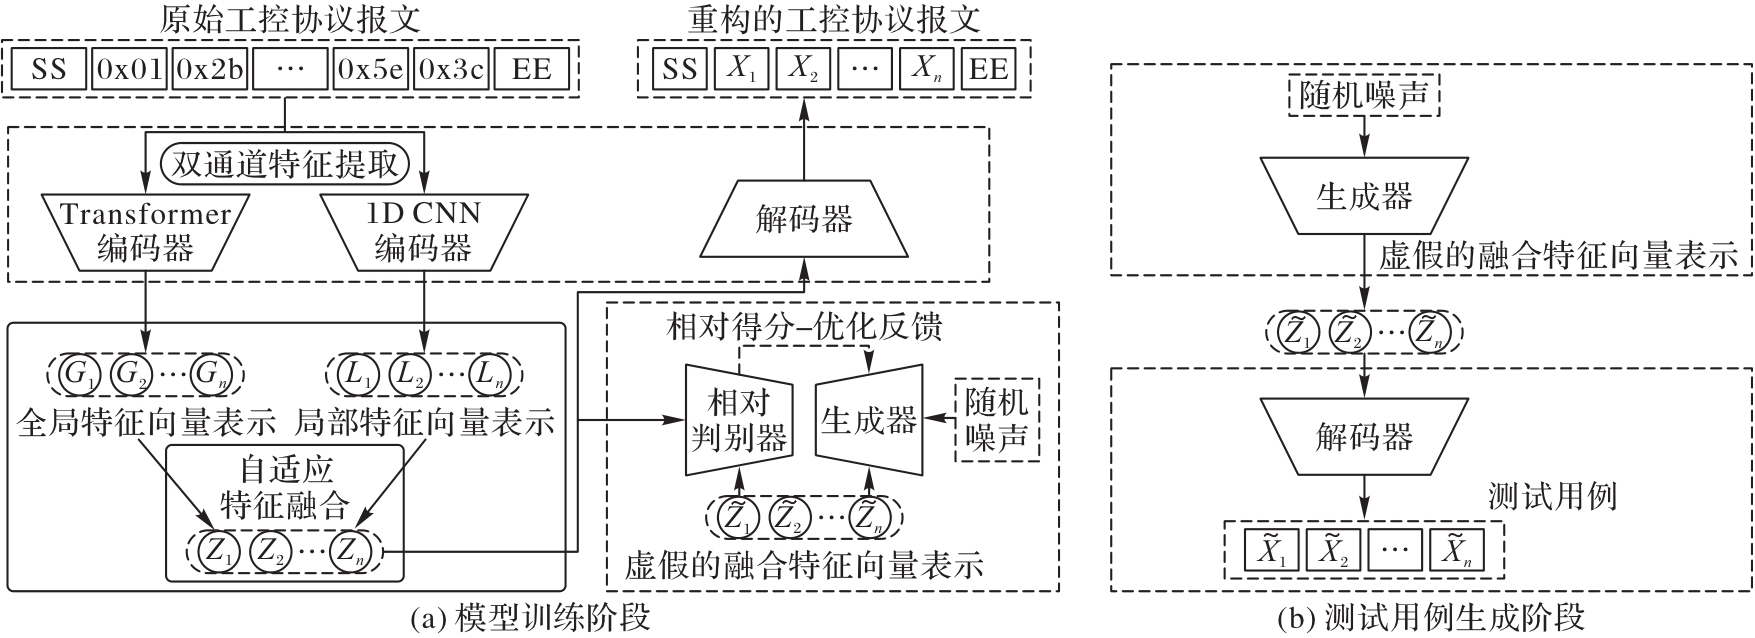
Fig. 2 Process of model training and test case generation
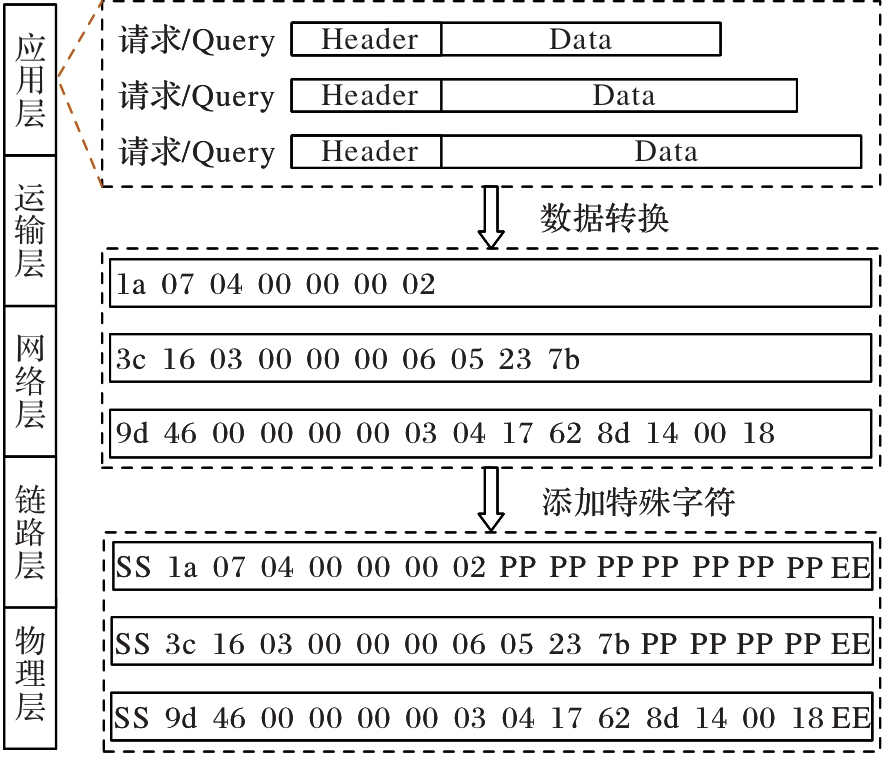
Fig. 3 Data preprocessing process
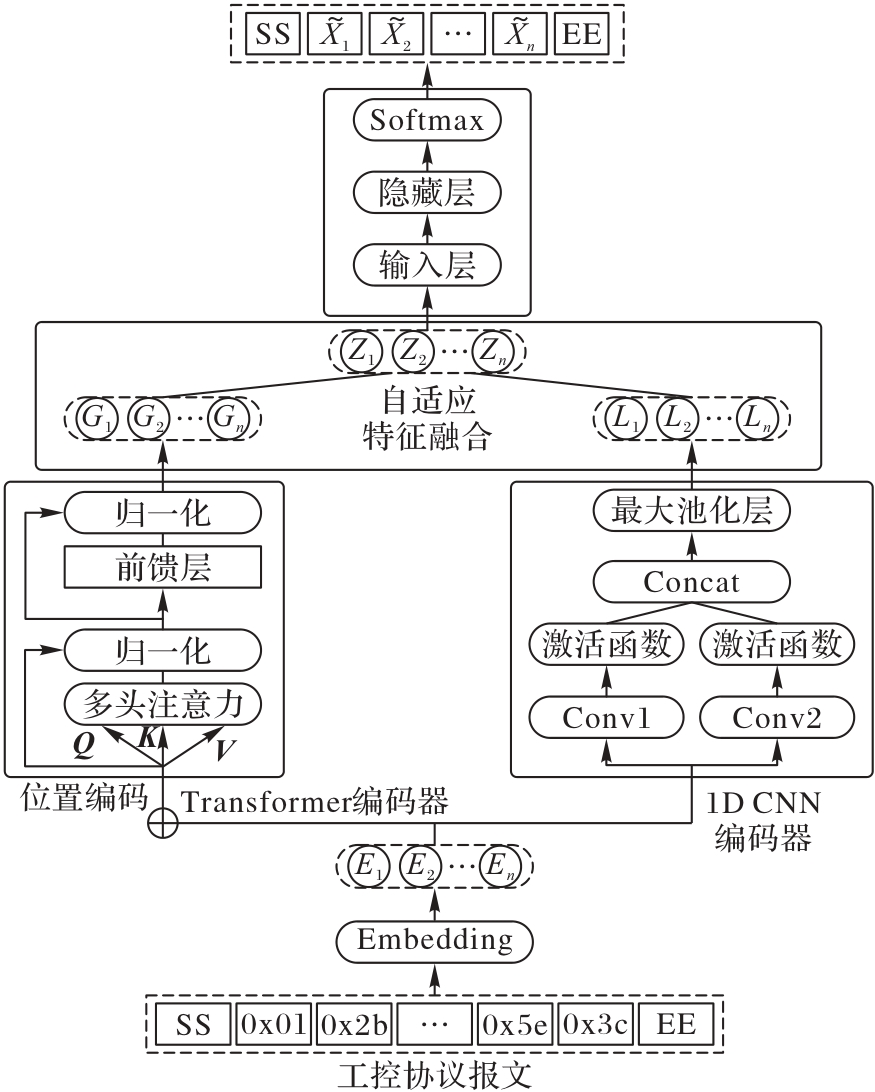
Fig. 4 Dual-channel semantic feature fusion of ICP
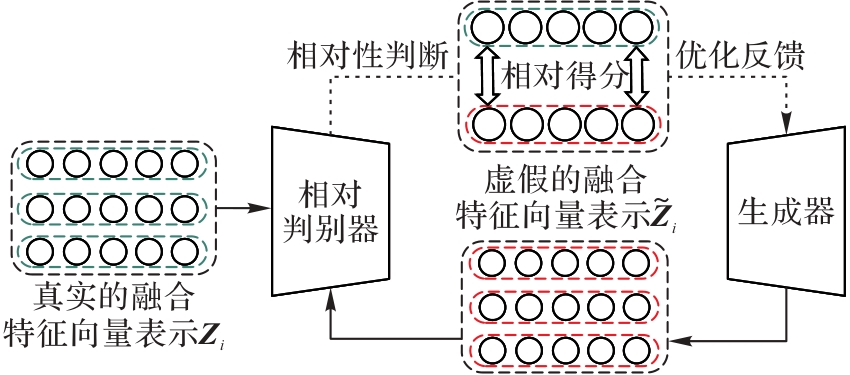
Fig. 5 Relativistic discriminator training strategy
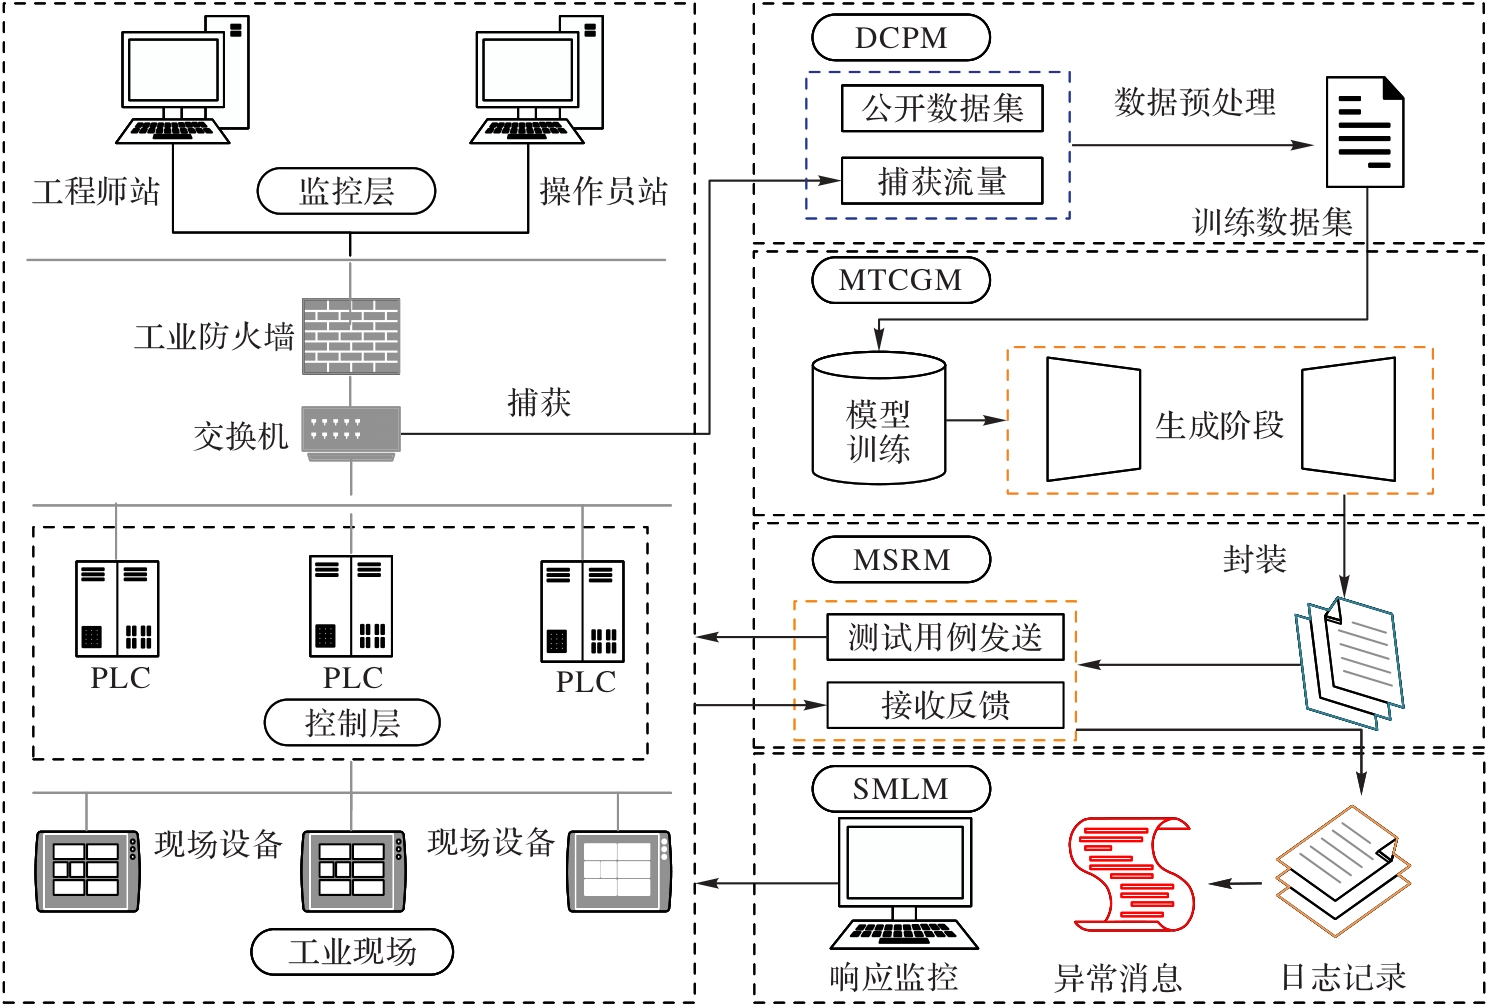
Fig. 6 Structure of DCSFFuzzer
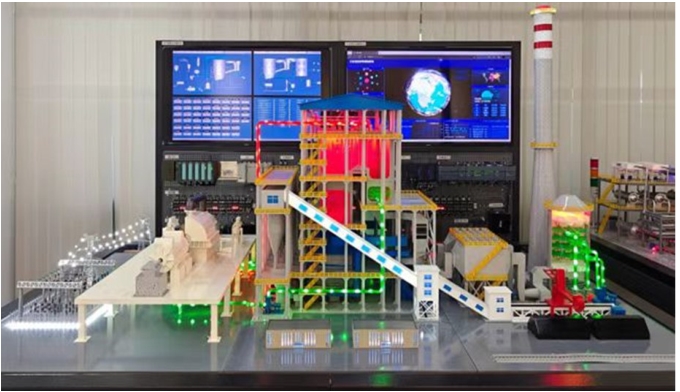
Fig. 7 Industrial attack and defense drill range
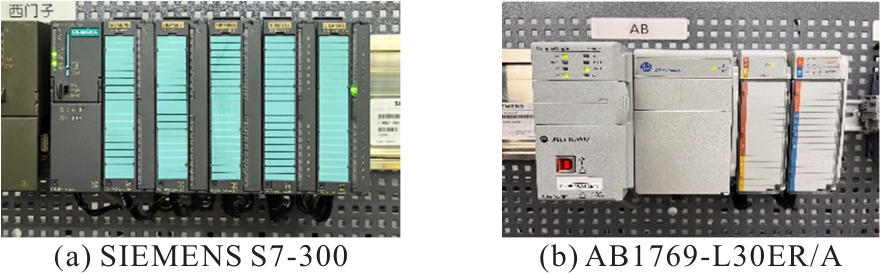
Fig. 8 Programmable logic controllers in experiments
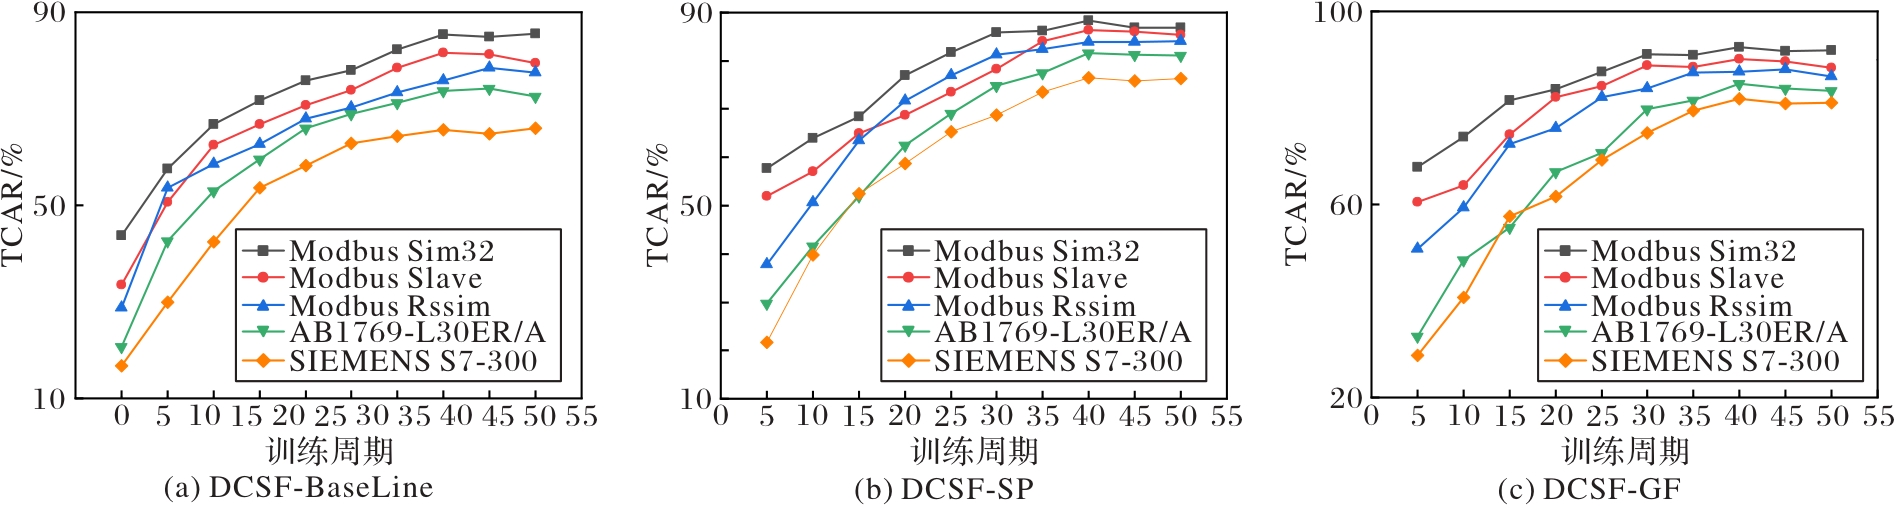
Fig. 9 Comparative experimental results of TCAR
| 测试模型 | 功能码 合法值占比 | 数据长度 合法值占比 | 功能码-数据长度匹配率 | TCAR |
|---|---|---|---|---|
| DCSF-BaseLine | 89.5 | 80.1 | 79.4 | 85.7 |
| DCSF-SP | 92.3 | 82.4 | 84.8 | 88.3 |
| DCSF-GF | 95.3 | 87.9 | 89.1 | 92.6 |
Tab. 1 Comparative experimental results of field validity and correlation indicators
| 测试模型 | 功能码 合法值占比 | 数据长度 合法值占比 | 功能码-数据长度匹配率 | TCAR |
|---|---|---|---|---|
| DCSF-BaseLine | 89.5 | 80.1 | 79.4 | 85.7 |
| DCSF-SP | 92.3 | 82.4 | 84.8 | 88.3 |
| DCSF-GF | 95.3 | 87.9 | 89.1 | 92.6 |
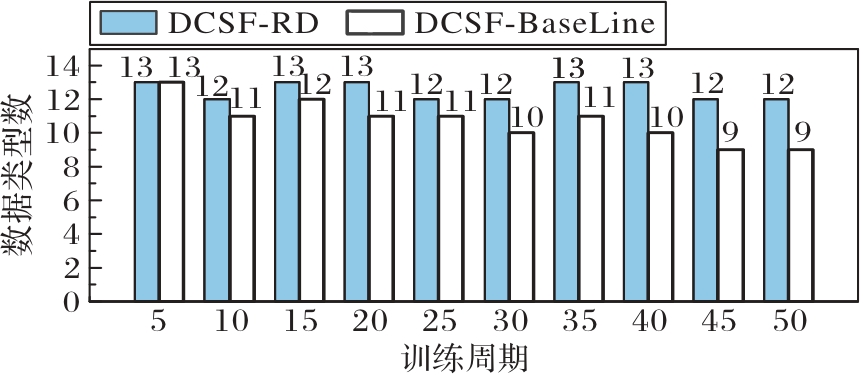
Fig. 10 Comparative experimental results of DGD
| Transformer层数 | 注意力头数 | GRU层数 | TCAR/% |
|---|---|---|---|
| 2 | 8 | 1 | 88.1 |
| 2 | 88.4 | ||
| 12 | 1 | 87.5 | |
| 2 | 87.9 | ||
| 4 | 8 | 1 | 88.6 |
| 2 | 89.1 | ||
| 12 | 1 | 87.6 | |
| 2 | 88.2 | ||
| 6 | 8 | 1 | 86.8 |
| 2 | 87.9 | ||
| 12 | 1 | 86.7 | |
| 2 | 86.6 |
Tab. 2 Comparative experimental results of model parameters
| Transformer层数 | 注意力头数 | GRU层数 | TCAR/% |
|---|---|---|---|
| 2 | 8 | 1 | 88.1 |
| 2 | 88.4 | ||
| 12 | 1 | 87.5 | |
| 2 | 87.9 | ||
| 4 | 8 | 1 | 88.6 |
| 2 | 89.1 | ||
| 12 | 1 | 87.6 | |
| 2 | 88.2 | ||
| 6 | 8 | 1 | 86.8 |
| 2 | 87.9 | ||
| 12 | 1 | 86.7 | |
| 2 | 86.6 |
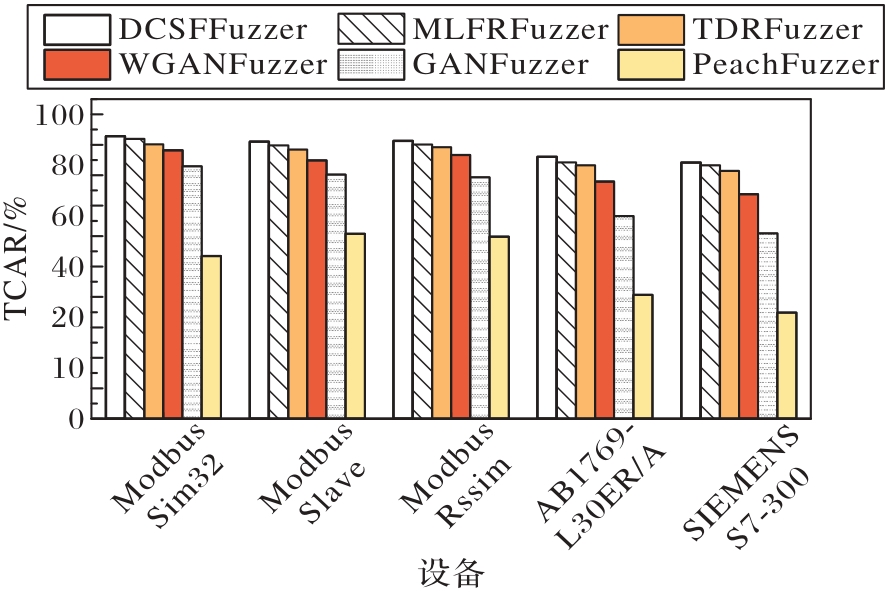
Fig. 11 Comparison results of TCAR across different frameworks
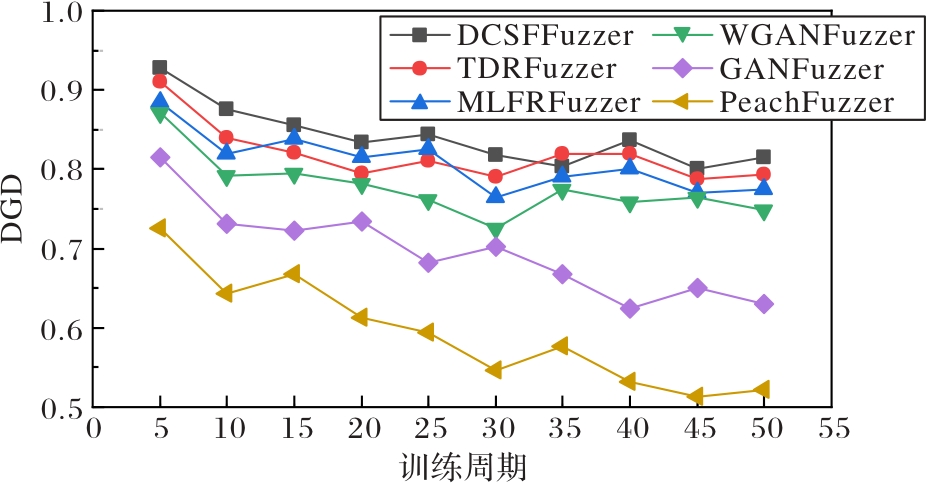
Fig. 12 Comparison results of DGD across different frameworks
| 测试框架 | 训练时间/h | 测试用例数 | 测试目标 | 异常数 | TTAR/% | 触发异常种类数 |
|---|---|---|---|---|---|---|
| DCSFFuzzer | 12.48 | 30 000 | Modbus Sim32 | 163 | 0.543 | 8 |
| Modbus Slave | 46 | 0.146 | 7 | |||
| Modbus Rssim | 62 | 0.210 | 8 | |||
| AB1769-L30ER/A | 14 | 0.046 | 6 | |||
| SIEMENS S7-300 | 12 | 0.040 | 5 | |||
| TDRFuzzer | 12.68 | 30 000 | Modbus Sim32 | 155 | 0.517 | 7 |
| Modbus Slave | 46 | 0.153 | 8 | |||
| Modbus Rssim | 58 | 0.193 | 6 | |||
| AB1769-L30ER/A | 13 | 0.043 | 6 | |||
| SIEMENS S7-300 | 12 | 0.040 | 5 | |||
| MLFRFuzzer | 13.15 | 30 000 | Modbus Sim32 | 151 | 0.500 | 7 |
| Modbus Slave | 44 | 0.146 | 6 | |||
| Modbus Rssim | 57 | 0.190 | 7 | |||
| AB1769-L30ER/A | 12 | 0.040 | 5 | |||
| SIEMENS S7-300 | 13 | 0.043 | 5 | |||
| WGANFuzzer | 13.37 | 30 000 | Modbus Sim32 | 135 | 0.450 | 7 |
| Modbus Slave | 40 | 0.133 | 6 | |||
| Modbus Rssim | 52 | 0.170 | 7 | |||
| AB1769-L30ER/A | 11 | 0.036 | 5 | |||
| SIEMENS S7-300 | 9 | 0.030 | 4 | |||
| GANFuzzer | 15.93 | 30 000 | Modbus Sim32 | 120 | 0.400 | 5 |
| Modbus Slave | 33 | 0.110 | 7 | |||
| Modbus Rssim | 35 | 0.116 | 6 | |||
| AB1769-L30ER/A | 8 | 0.027 | 3 | |||
| SIEMENS S7-300 | 6 | 0.020 | 3 | |||
| PeachFuzzer | — | 30 000 | Modbus Sim32 | 103 | 0.340 | 2 |
| Modbus Slave | 26 | 0.086 | 1 | |||
| Modbus Rssim | 35 | 0.116 | 2 | |||
| AB1769-L30ER/A | 6 | 0.020 | 1 | |||
| SIEMENS S7-300 | 4 | 0.013 | 1 |
Tab. 3 Comparative results of TTAR
| 测试框架 | 训练时间/h | 测试用例数 | 测试目标 | 异常数 | TTAR/% | 触发异常种类数 |
|---|---|---|---|---|---|---|
| DCSFFuzzer | 12.48 | 30 000 | Modbus Sim32 | 163 | 0.543 | 8 |
| Modbus Slave | 46 | 0.146 | 7 | |||
| Modbus Rssim | 62 | 0.210 | 8 | |||
| AB1769-L30ER/A | 14 | 0.046 | 6 | |||
| SIEMENS S7-300 | 12 | 0.040 | 5 | |||
| TDRFuzzer | 12.68 | 30 000 | Modbus Sim32 | 155 | 0.517 | 7 |
| Modbus Slave | 46 | 0.153 | 8 | |||
| Modbus Rssim | 58 | 0.193 | 6 | |||
| AB1769-L30ER/A | 13 | 0.043 | 6 | |||
| SIEMENS S7-300 | 12 | 0.040 | 5 | |||
| MLFRFuzzer | 13.15 | 30 000 | Modbus Sim32 | 151 | 0.500 | 7 |
| Modbus Slave | 44 | 0.146 | 6 | |||
| Modbus Rssim | 57 | 0.190 | 7 | |||
| AB1769-L30ER/A | 12 | 0.040 | 5 | |||
| SIEMENS S7-300 | 13 | 0.043 | 5 | |||
| WGANFuzzer | 13.37 | 30 000 | Modbus Sim32 | 135 | 0.450 | 7 |
| Modbus Slave | 40 | 0.133 | 6 | |||
| Modbus Rssim | 52 | 0.170 | 7 | |||
| AB1769-L30ER/A | 11 | 0.036 | 5 | |||
| SIEMENS S7-300 | 9 | 0.030 | 4 | |||
| GANFuzzer | 15.93 | 30 000 | Modbus Sim32 | 120 | 0.400 | 5 |
| Modbus Slave | 33 | 0.110 | 7 | |||
| Modbus Rssim | 35 | 0.116 | 6 | |||
| AB1769-L30ER/A | 8 | 0.027 | 3 | |||
| SIEMENS S7-300 | 6 | 0.020 | 3 | |||
| PeachFuzzer | — | 30 000 | Modbus Sim32 | 103 | 0.340 | 2 |
| Modbus Slave | 26 | 0.086 | 1 | |||
| Modbus Rssim | 35 | 0.116 | 2 | |||
| AB1769-L30ER/A | 6 | 0.020 | 1 | |||
| SIEMENS S7-300 | 4 | 0.013 | 1 |
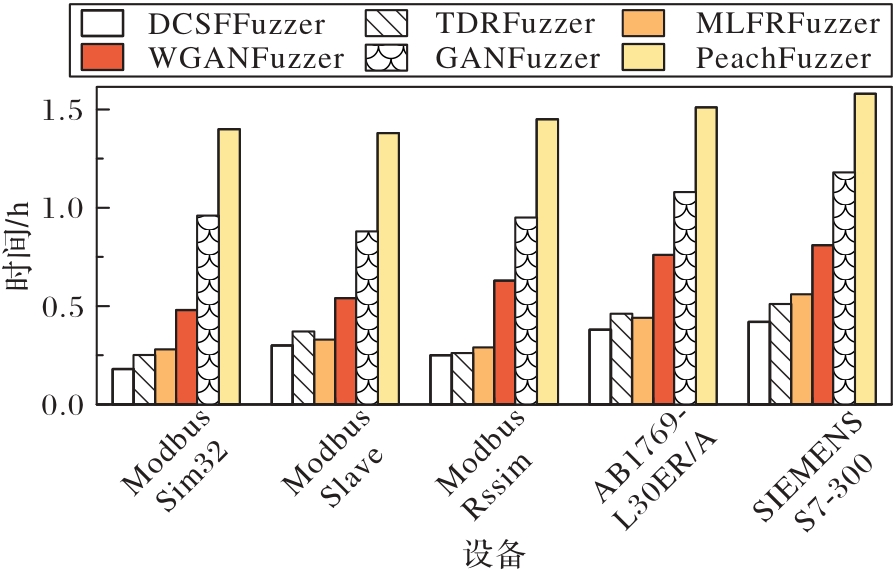
Fig. 13 Comparison results of TDFV across different frameworks
| 异常类型 | Modbus Sim32 | Modbus Slave | Modbus Rssim | AB1769-L30ER/A | SIEMENS S7-300 |
|---|---|---|---|---|---|
| 异常功能码 | | | | | |
| 非法数据地址 | | | |||
| 断开连接 | | | | | |
| 停止运行 | | | |||
| 文件未找到 | | | | ||
| XX从站无响应 | | | | ||
| 数据长度不符 | | | | | |
| 拒绝服务 | |
Tab. 4 Anomalies triggered by DCSFFuzzer
| 异常类型 | Modbus Sim32 | Modbus Slave | Modbus Rssim | AB1769-L30ER/A | SIEMENS S7-300 |
|---|---|---|---|---|---|
| 异常功能码 | | | | | |
| 非法数据地址 | | | |||
| 断开连接 | | | | | |
| 停止运行 | | | |||
| 文件未找到 | | | | ||
| XX从站无响应 | | | | ||
| 数据长度不符 | | | | | |
| 拒绝服务 | |
| [1] | Wei X, Yan Z, Liang X. A survey on fuzz testing technologies for industrial control protocols [J]. Journal of Network and Computer Applications, 2024, 232: No.104020. |
| [2] | Huang L, Zhao P, Chen H, et al. Large language models based fuzzing techniques: a survey [PP/OL]. V2. arXiv (2024-02-07) [2025-01-30].. |
| [3] | Yang L, Wei C, Yang J, et al. FuzzCoder: code large language model-based fuzz testing for industrial IoT programs [J]. IEEE Internet of Things Journal, 2025, 12(18): 36842-36851. |
| [4] | Wang Z, Zhang Y, Chen Y, et al. A survey on programmable logic controller vulnerabilities, attacks, detections, and forensics [J]. Processes, 2023, 11(3): No.918. |
| [5] | Wang W, Chen Z, Zheng Z, et al. MTA Fuzzer: a low-repetition rate Modbus TCP fuzzing method based on Transformer and Mutation Target Adaptation [J]. Computers and Security, 2024, 144: No.103973. |
| [6] | Sun J, Yin Z, Zhang H, et al. Adversarial generation method for smart contract fuzz testing seeds guided by chain-based LLM [J]. Automated Software Engineering, 2025, 32: No.12. |
| [7] | Yang H, Huang Y, Zhang Z, et al. A novel generative adversarial network-based fuzzing cases generation method for industrial control system protocols [J]. Computers and Electrical Engineering, 2024, 117: No.109268. |
| [8] | 宗学军,韩冰,王国刚,等. 基于自适应动态区间策略的工业控制协议模糊测试方法TDRFuzzer[J]. 计算机应用, 2025, 45(10): 3241-3251. |
| Zong Xuejun, Han Bing, Wang Guogang, et al. TDRFuzzer: fuzzing method for industrial control protocols based on adaptive dynamic interval strategy [J]. Journal of Computer Applications, 2025, 45(10): 3241-3251. | |
| [9] | Aldysty A R, Moustafa N, Lakshika E. A holistic review of fuzzing for vulnerability assessment in industrial network protocols [J]. IEEE Open Journal of the Communications Society, 2025, 6: 4437-4461. |
| [10] | 连莲,孙世明,王国刚,等. 基于多尺度潜在特征表示的工业控制协议模糊测试方法 [J]. 计算机应用研究, 2025, 42(2): 545-554. |
| Lian Lian, Sun Shiming, Wang Guogang, et al. Industrial control protocols fuzz testing method based on multi-scale latent feature representation [J]. Application Research of Computers, 2025, 42(2): 545-554. | |
| [11] | 徐鹏,刘嘉勇,林波,等. 基于循环神经网络的模糊测试用例生成[J]. 计算机应用研究, 2019, 36(9): 2679-2685. |
| Xu Peng, Liu Jiayong, Lin Bo, et al. Generation of fuzzing test case based on recurrent neural networks [J]. Application Research of Computers, 2019, 36(9): 2679-2685. | |
| [12] | Zhao H, Li Z, Wei H, et al. SeqFuzzer: an industrial protocol fuzzing framework from a deep learning perspective [C]// ICST 2019. Piscataway: IEEE, 2019: 59-67. |
| [13] | Hu Z, Shi J, Huang Y, et al. GANFuzz: a GAN-based industrial network protocol fuzzing framework [C]// CF 2018. New York: ACM, 2018: 138-145. |
| [14] | Yu Z, Wang H, Wang D, et al. CGFuzzer: a fuzzing approach based on coverage-guided generative adversarial networks for industrial IoT protocols [J]. IEEE Internet of Things Journal, 2022, 9(21): 21607-21619. |
| [15] | Wang W, Chen Z, Zheng Z, et al. An adaptive fuzzing method based on Transformer and protocol similarity mutation [J]. Computers and Security, 2023, 129: No.103197. |
| [16] | Dey R, Salem F M. Gate-variants of Gated Recurrent Unit (GRU) neural networks [C]// MWSCAS 2017. Piscataway: IEEE, 2017: 1597-1600. |
| [17] | Miller B P, Fredriksen L, So B. An empirical study of the reliability of UNIX utilities [J]. Communications of the ACM, 1990, 33(12): 32-44. |
| [18] | Si X, Song Y, Sun X, et al. MARLFuzz: industrial control protocols fuzzing based on multi-agent reinforcement learning [J]. Computing, 2025, 107(2): No.61. |
| [19] | Mallissery S, Wu Y S. Demystify the fuzzing methods: a comprehensive survey [J]. ACM Computing Surveys, 2024, 56(3): No.71. |
| [20] | 徐航,杨智,陈性元,等. 基于自适应敏感区域变异的覆盖引导模糊测试[J]. 计算机应用, 2024, 44(8): 2528-2535. |
| Xu Hang, Yang Zhi, Chen Xingyuan, et al. Coverage-guided fuzzing based on adaptive sensitive region mutation [J]. Journal of Computer Applications, 2024, 44(8): 2528-2535. | |
| [21] | Li Z, Zhao H, Shi J, et al. An intelligent fuzzing data generation method based on deep adversarial learning [J]. IEEE Access, 2019, 7: 49327-49340. |
| [22] | Wanyan H, Lai Y, Liu J, et al. NCMFuzzer: using non-critical field mutation and test case combination to improve the efficiency of ICS protocol fuzzing [J]. Computers and Security, 2024, 141: No.103811. |
| [23] | Chen L, Wang Y, Xiang X, et al. TXL-Fuzz: a long attention mechanism-based fuzz testing model for industrial IoT protocols[J]. IEEE Internet of Things Journal, 2024, 11(23): 38238-38245. |
| [24] | Li Z, Liu F, Yang W, et al. A survey of convolutional neural networks: analysis, applications, and prospects [J]. IEEE Transactions on Neural Networks and Learning Systems, 2022, 33(12): 6999-7019. |
| [25] | Vaswani A, Shazeer N, Parmar N, et al. Attention is all you need[C]// NeurIPS 2017. Red Hook: Curran Associates Inc., 2017: 6000-6010. |
| [26] | Creswell A, White T, Dumoulin V, et al. Generative adversarial networks: an overview [J]. IEEE Signal Processing Magazine, 2018, 35(1): 53-65. |
| [27] | Zong X, Luo W, Ning B, et al. DiffusionFuzz: fuzzing framework of industrial control protocols based on denoising diffusion probabilistic model [J]. IEEE Access, 2024, 12: 67795-67808. |
| [28] | Onyekpe U, Palade V, Kanarachos S,et al. A quaternion gated recurrent unit neural network for sensor fusion [J]. Sensors, 2021, 12(3): No.117. |
| [29] | Jolicoeur-Martineau A. The relativistic discriminator: a key element missing from standard GAN [PP/OL]. V3. arXiv (2018-09-10) [2025-06-21].. |
| [30] | Lemay A, Fernandez J M. Providing SCADA network data sets for intrusion detection research [C]// CSET 16. Berkeley: USENIX Association, 2016: 1-8. |
| [1] | Jiangyan CHEN, Yandan WANG, Yihu LIU, Yinglong MA. Collaborative query optimization-based framework for long-tailed object detection [J]. Journal of Computer Applications, 2026, 46(9): 2769-2775. |
| [2] | Yifan WANG, Hu HAN, Dong LI, Yating FAN, Lin LI. Heterogeneous enhancement and multi-source knowledge fusion for aspect-based sentiment analysis [J]. Journal of Computer Applications, 2026, 46(9): 2752-2760. |
| [3] | Dingli YANG, Yuanfang WEI, Wenrui HU, Liyang KONG, Yinshan YU. Spatio-temporal modeling and hierarchical feature enhancement for person re-identification [J]. Journal of Computer Applications, 2026, 46(9): 2776-2786. |
| [4] | Lin HUANG, Yingshun LI, Weiyan TONG, Shuyuan ZHANG, Zihan WANG. Remote sensing image object detection algorithm based on improved real-time detection Transformer [J]. Journal of Computer Applications, 2026, 46(8): 2652-2659. |
| [5] | Ming LIU, Dongqi SHEN, Ziyang MENG. Point cloud registration network with dual-branch multi-level feature fusion [J]. Journal of Computer Applications, 2026, 46(8): 2584-2593. |
| [6] | Jiangyu YAN, Shiqian WANG, Hong WANG. Electricity theft detection method based on improved Wasserstein generative adversarial network with gradient penalty and time-frequency feature fusion [J]. Journal of Computer Applications, 2026, 46(8): 2691-2698. |
| [7] | Guoyou ZHANG, Hongyu NIE, Lihu PAN, Rundong LEI. Point-MLPBLS: point cloud semantic segmentation network based on MLP cascaded broad learning system [J]. Journal of Computer Applications, 2026, 46(7): 2259-2266. |
| [8] | Lili HE, Meng CAO, Lei ZHANG, Hongjun PAN, Yi LIU, Chengxin SUN. Sign language generation model based on Kolmogorov-Arnold network and diffusion Transformer [J]. Journal of Computer Applications, 2026, 46(6): 1801-1810. |
| [9] | Songhao ZHU, Zhiyun ZHAO, Mengling WANG. Low-light image enhancement network based on lightweight residual and brightness-aware dynamic feature fusion [J]. Journal of Computer Applications, 2026, 46(6): 1936-1946. |
| [10] | Wenjun FENG, Xinwei SONG, Yuntao YUE. Time series prediction of environmental electric field intensity with generalized correlation entropy loss function-based Transformer model [J]. Journal of Computer Applications, 2026, 46(6): 1872-1880. |
| [11] | Chao LYU, Geyao MA. Lightweight human pose estimation network based on redundant feature suppression [J]. Journal of Computer Applications, 2026, 46(6): 1973-1980. |
| [12] | Jun QIN, Xintao JIAO, Biqing ZENG. Non-intrusive load monitoring method combining BiLSTM-Transformer and Kolmogorov-Arnold network [J]. Journal of Computer Applications, 2026, 46(6): 2026-2033. |
| [13] | Yuanhao HE, Jun ZHAO. Defect detection algorithm for train bearing rollers based on FHC-DETR [J]. Journal of Computer Applications, 2026, 46(5): 1624-1633. |
| [14] | Xuechao LIAO, Rui CHEN. Prediction-evaluation framework for anomaly detection in electric vehicle lithium-ion battery [J]. Journal of Computer Applications, 2026, 46(5): 1614-1623. |
| [15] | Hongrui ZHANG, Weiming FENG, Luxia YANG, Yongjie MA. CSAF-YOLO: improved YOLO11 algorithm for underwater small object detection [J]. Journal of Computer Applications, 2026, 46(5): 1578-1585. |
| Viewed | ||||||
|
Full text |
|
|||||
|
Abstract |
|
|||||
