


Journal of Computer Applications ›› 2026, Vol. 46 ›› Issue (9): 2867-2876.DOI: 10.11772/j.issn.1001-9081.2025081040
• Cyber security • Previous Articles
Lixia XIE1, Chaoyue CAO2, Hongyu YANG1,2( )
Received:2025-09-09
Revised:2025-11-05
Accepted:2025-11-10
Online:2025-11-17
Published:2026-09-10
Contact:
Hongyu YANG
About author:XIE Lixia, born in 1974, M. S., professor. Her research interests include network information security.Supported by:
谢丽霞1, 曹超越2, 杨宏宇1,2()
通讯作者:
杨宏宇
作者简介:谢丽霞(1974—),女,重庆人,教授,硕士,CCF高级会员,主要研究方向:网络信息安全基金资助:CLC Number:
Lixia XIE, Chaoyue CAO, Hongyu YANG. ADS-B attack detection method based on improved DeepLabV3+[J]. Journal of Computer Applications, 2026, 46(9): 2867-2876.
谢丽霞, 曹超越, 杨宏宇. 基于改进DeepLabV3+的ADS-B攻击检测方法[J]. 《计算机应用》唯一官方网站, 2026, 46(9): 2867-2876.
Add to citation manager EndNote|Ris|BibTeX
URL: https://www.joca.cn/EN/10.11772/j.issn.1001-9081.2025081040
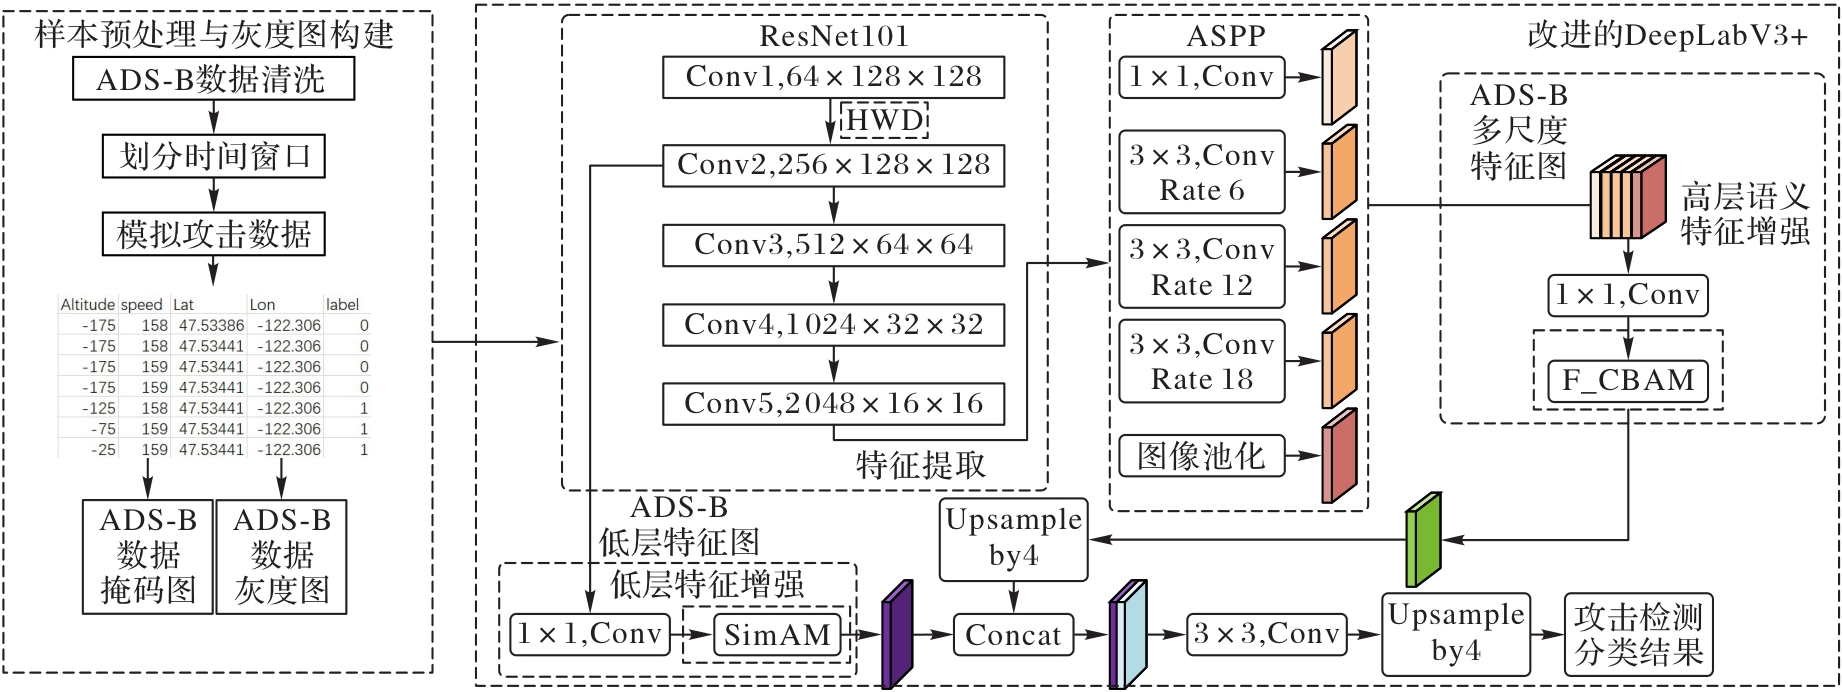
Fig. 1 Framework of proposed method
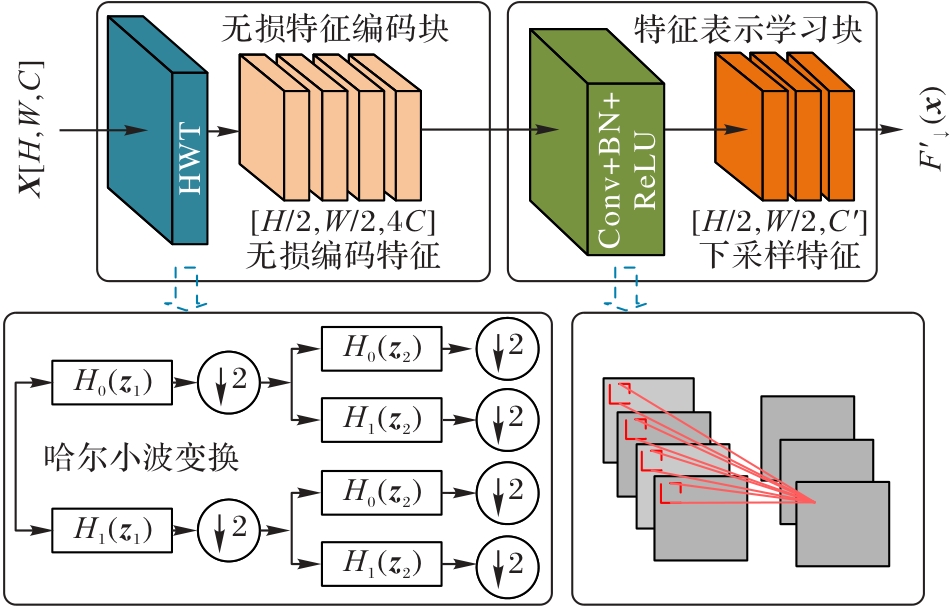
Fig. 2 Architecture of HWD module
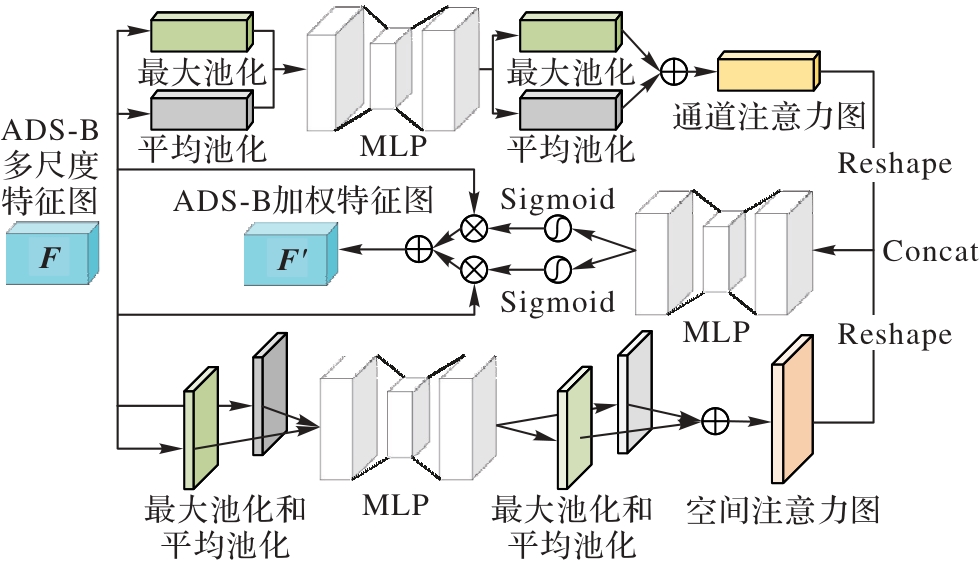
Fig. 3 Structure of improved CBAM attention mechanism
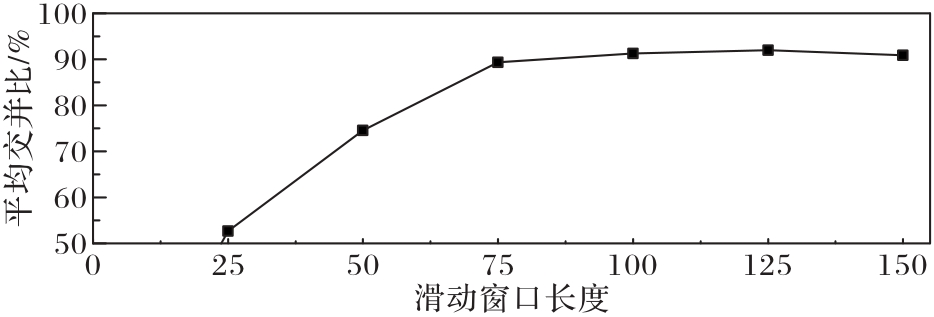
Fig. 4 Sliding window length selection
| 方法 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|
| LSTM-ED[ | 86.61 | 91.64 | 88.04 |
| VAE-SVDD[ | 87.43 | 90.58 | 88.59 |
| GAN-LSTM[ | 86.88 | 88.84 | 87.25 |
| TTSAD[ | 87.85 | 90.46 | 88.43 |
| DeepLabV3+[ | 96.79 | 95.80 | 96.26 |
| 本文方法 | 98.79 | 98.21 | 98.48 |
Tab. 1 Performance comparison of different methods in attack detection binary classification tasks
| 方法 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|
| LSTM-ED[ | 86.61 | 91.64 | 88.04 |
| VAE-SVDD[ | 87.43 | 90.58 | 88.59 |
| GAN-LSTM[ | 86.88 | 88.84 | 87.25 |
| TTSAD[ | 87.85 | 90.46 | 88.43 |
| DeepLabV3+[ | 96.79 | 95.80 | 96.26 |
| 本文方法 | 98.79 | 98.21 | 98.48 |
| 攻击类型 | 评估指标 | U-Net[ | SegFormer[ | K-Net[ | Fast-SCNN[ | DeepLabV3+[ | 本文方法 |
|---|---|---|---|---|---|---|---|
| 高度偏移 | 精确率 | 93.82 | 84.00 | 92.39 | 53.64 | 93.26 | 96.24 |
| 召回率 | 80.51 | 83.17 | 74.60 | 84.08 | 85.55 | 95.43 | |
| F1分数 | 86.66 | 83.59 | 82.55 | 65.50 | 89.24 | 95.83 | |
| 速度偏移 | 精确率 | 95.50 | 81.81 | 86.42 | 98.32 | 88.50 | 97.37 |
| 召回率 | 85.42 | 82.68 | 91.56 | 50.75 | 98.46 | 99.70 | |
| F1分数 | 90.18 | 82.24 | 88.92 | 66.94 | 93.21 | 98.52 | |
| 重放攻击 | 精确率 | 43.77 | 78.72 | 51.17 | 58.30 | 85.23 | 82.80 |
| 召回率 | 61.20 | 40.23 | 50.37 | 32.40 | 89.70 | 98.30 | |
| F1分数 | 51.04 | 53.25 | 50.76 | 41.65 | 87.41 | 89.89 | |
| 随机噪声 | 精确率 | 77.82 | 73.97 | 80.01 | 70.02 | 94.32 | 89.18 |
| 召回率 | 85.68 | 85.11 | 82.09 | 79.95 | 76.94 | 96.19 | |
| F1分数 | 81.56 | 79.15 | 81.03 | 74.65 | 84.75 | 92.55 | |
| 航迹异常 | 精确率 | 98.83 | 91.48 | 96.06 | 97.89 | 93.48 | 93.73 |
| 召回率 | 90.72 | 94.65 | 97.86 | 92.26 | 99.97 | 99.31 | |
| F1分数 | 94.60 | 93.04 | 96.95 | 94.99 | 96.62 | 96.44 | |
| DoS攻击 | 精确率 | 47.15 | 33.52 | 38.74 | 29.11 | 90.01 | 95.96 |
| 召回率 | 79.62 | 64.82 | 68.58 | 91.37 | 93.28 | 96.17 | |
| F1分数 | 59.23 | 44.19 | 49.51 | 44.16 | 91.62 | 96.07 | |
| 平均交并比 | 68.75 | 63.76 | 66.71 | 55.56 | 84.55 | 91.28 | |
Tab. 2 Performance comparison of different methods in attack detection multi-class classification tasks
| 攻击类型 | 评估指标 | U-Net[ | SegFormer[ | K-Net[ | Fast-SCNN[ | DeepLabV3+[ | 本文方法 |
|---|---|---|---|---|---|---|---|
| 高度偏移 | 精确率 | 93.82 | 84.00 | 92.39 | 53.64 | 93.26 | 96.24 |
| 召回率 | 80.51 | 83.17 | 74.60 | 84.08 | 85.55 | 95.43 | |
| F1分数 | 86.66 | 83.59 | 82.55 | 65.50 | 89.24 | 95.83 | |
| 速度偏移 | 精确率 | 95.50 | 81.81 | 86.42 | 98.32 | 88.50 | 97.37 |
| 召回率 | 85.42 | 82.68 | 91.56 | 50.75 | 98.46 | 99.70 | |
| F1分数 | 90.18 | 82.24 | 88.92 | 66.94 | 93.21 | 98.52 | |
| 重放攻击 | 精确率 | 43.77 | 78.72 | 51.17 | 58.30 | 85.23 | 82.80 |
| 召回率 | 61.20 | 40.23 | 50.37 | 32.40 | 89.70 | 98.30 | |
| F1分数 | 51.04 | 53.25 | 50.76 | 41.65 | 87.41 | 89.89 | |
| 随机噪声 | 精确率 | 77.82 | 73.97 | 80.01 | 70.02 | 94.32 | 89.18 |
| 召回率 | 85.68 | 85.11 | 82.09 | 79.95 | 76.94 | 96.19 | |
| F1分数 | 81.56 | 79.15 | 81.03 | 74.65 | 84.75 | 92.55 | |
| 航迹异常 | 精确率 | 98.83 | 91.48 | 96.06 | 97.89 | 93.48 | 93.73 |
| 召回率 | 90.72 | 94.65 | 97.86 | 92.26 | 99.97 | 99.31 | |
| F1分数 | 94.60 | 93.04 | 96.95 | 94.99 | 96.62 | 96.44 | |
| DoS攻击 | 精确率 | 47.15 | 33.52 | 38.74 | 29.11 | 90.01 | 95.96 |
| 召回率 | 79.62 | 64.82 | 68.58 | 91.37 | 93.28 | 96.17 | |
| F1分数 | 59.23 | 44.19 | 49.51 | 44.16 | 91.62 | 96.07 | |
| 平均交并比 | 68.75 | 63.76 | 66.71 | 55.56 | 84.55 | 91.28 | |
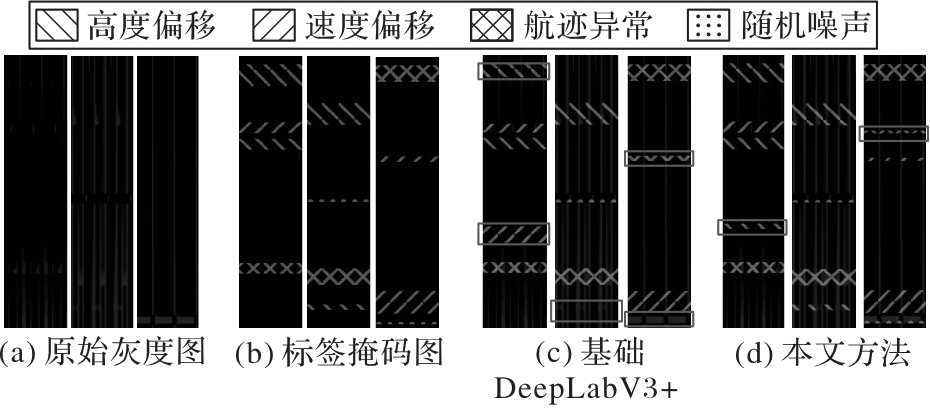
Fig. 5 Visualized experimental results of different methods
| 方法 | 主干网络 | mIoU | mPrecision | mRecall |
|---|---|---|---|---|
| DeepLabV3+ | ResNet101 | 75.20 | 85.22 | 83.28 |
| DeepLabV3+HWD | ResNet101 | 81.05 | 86.23 | 90.50 |
Tab. 3 Experimental results of ResNet101 module improvement
| 方法 | 主干网络 | mIoU | mPrecision | mRecall |
|---|---|---|---|---|
| DeepLabV3+ | ResNet101 | 75.20 | 85.22 | 83.28 |
| DeepLabV3+HWD | ResNet101 | 81.05 | 86.23 | 90.50 |
| 注意力机制 | mIoU | mPrecision | mRecall |
|---|---|---|---|
| SimAM | 83.22 | 87.55 | 91.80 |
| EANet | 82.85 | 86.67 | 90.78 |
| ECA | 81.95 | 86.35 | 90.13 |
| CBAM | 82.50 | 87.36 | 91.82 |
| F_CBAM | 83.75 | 88.15 | 92.32 |
Tab. 4 Comparative experimental results of different attention mechanisms
| 注意力机制 | mIoU | mPrecision | mRecall |
|---|---|---|---|
| SimAM | 83.22 | 87.55 | 91.80 |
| EANet | 82.85 | 86.67 | 90.78 |
| ECA | 81.95 | 86.35 | 90.13 |
| CBAM | 82.50 | 87.36 | 91.82 |
| F_CBAM | 83.75 | 88.15 | 92.32 |
| ResNet101 | SimAM | EANet | ECA | CBAM | F_ CBAM | HWD | mIoU | mPrecision |
|---|---|---|---|---|---|---|---|---|
| | | | | 84.85 | 87.82 | |||
| | | | | 84.25 | 88.55 | |||
| | | | | 91.28 | 93.25 | |||
| | | | | 83.25 | 87.26 | |||
| | | | | 83.60 | 89.35 | |||
| | | | | 86.68 | 91.66 |
Tab. 5 Comparative experimental results of different module combinations
| ResNet101 | SimAM | EANet | ECA | CBAM | F_ CBAM | HWD | mIoU | mPrecision |
|---|---|---|---|---|---|---|---|---|
| | | | | 84.85 | 87.82 | |||
| | | | | 84.25 | 88.55 | |||
| | | | | 91.28 | 93.25 | |||
| | | | | 83.25 | 87.26 | |||
| | | | | 83.60 | 89.35 | |||
| | | | | 86.68 | 91.66 |
| [1] | Khan H A, Khan H, Ghafoor S, et al. A survey on security of Automatic Dependent Surveillance-Broadcast (ADS-B) protocol: challenges, potential solutions and future directions [J]. IEEE Communications Surveys and Tutorials, 2025, 27(5): 3199-3226. |
| [2] | Wu Z, Shang T, Guo A. Security issues in Automatic Dependent Surveillance-Broadcast (ADS-B): a survey [J]. IEEE Access, 2020, 8: 122147-122167. |
| [3] | Strohmeier M, Lenders V, Martinovic I. On the security of the automatic dependent surveillance-broadcast protocol [J]. IEEE Communications Surveys and Tutorials, 2015, 17(2): 1066-1087. |
| [4] | 杨宏宇,张恒鸣,朱友文,等. 面向LBS的ADS-B报文定位数据本地化差分隐私保护方法[J]. 网络与信息安全学报, 2025, 11(4): 32-49. |
| Yang Hongyu, Zhang Hengming, Zhu Youwen, et al. Differential privacy protection method for localization of ADS-B message positioning data oriented to LBS [J]. Chinese Journal of Network and Information Security, 2025, 11(4): 32-49. | |
| [5] | Çevik N, Akleylek S. Sok of machine learning and deep learning based anomaly detection methods for automatic dependent surveillance-broadcast [J]. IEEE Access, 2024, 12: 35643-35662. |
| [6] | Corrado S J, Puranik T G, Fischer O P, et al. A clustering-based quantitative analysis of the interdependent relationship between spatial and energy anomalies in ADS-B trajectory data [J]. Transportation Research Part C: Emerging Technologies, 2021, 131: No.103331. |
| [7] | 王布宏,罗鹏,阳勇,等. 空中交通管理系统网络安全研究综述与展望[J]. 电子与信息学报, 2025, 47(5): 1230-1265. |
| Wang Buhong, Luo Peng, Yang Yong, et al. A review and prospect of cybersecurity research on air traffic management systems [J]. Journal of Electronics and Information Technology, 2025, 47(5): 1230-1265. | |
| [8] | Melvyn P, Couturier R, Ambert F, et al. Detecting ghost aircraft flooding in the surveillance of low-flying civil and military aircraft[C]// ICCCR 2024. Piscataway: IEEE, 2024: 328-332. |
| [9] | Zhang X, Li J. SR-GNN: spectral residuals with graph neural networks for anomaly detection in ADS-B data [C]// FCS 2023, CCIS 1992. Singapore: Springer, 2024: 503-516. |
| [10] | Vajrobol V, Saxena G J, Singh S, et al. Enhancing aviation control security through ADS-B injection detection using ensemble meta-learning models with explainable AI [J]. Alexandria Engineering Journal, 2025, 112: 63-73. |
| [11] | Habler E, Shabtai A. Using LSTM encoder-decoder algorithm for detecting anomalous ADS-B messages [J]. Computers and Security, 2018, 78: 155-173. |
| [12] | Habler E, Shabtai A. Analyzing sequences of airspace states to detect anomalous traffic conditions [J]. IEEE Transactions on Aerospace and Electronic Systems, 2022, 58(3): 1843-1857. |
| [13] | Ji Y, Wang L, Wu W, et al. A method for LSTM-based trajectory modeling and abnormal trajectory detection [J]. IEEE Access, 2020, 8: 104063-104073. |
| [14] | Yue M, Zheng H, Cui H, et al. GAN-LSTM-based ADS-B attack detection in the context of air traffic control [J]. IEEE Internet of Things Journal, 2023, 10(14): 12651-12665. |
| [15] | Joseph N S, Banerjee C, Pasiliao E, et al. FlightSense: a spoofer detection and aircraft identification system using raw ADS-B data[C]// Big Data 2020. Piscataway: IEEE, 2020: 3885-3894. |
| [16] | Heiselberg P, Sørensen K A, Heiselberg H. Aircraft detection and state estimation [C]// IGARSS 2024. Piscataway: IEEE, 2024: 7693-7696. |
| [17] | Luo P, Wang B, Tian J. TTSAD: TCN-Transformer-SVDD model for Anomaly Detection in air traffic ADS-B data [J]. Computers and Security, 2024, 141: No.103840. |
| [18] | Cai K, Di Z, Zhu Y, et al. An attention-based convolutional network framework for detection and localization of GNSS interference sources [J]. IEEE Transactions on Aerospace and Electronic Systems, 2024, 60(3): 2995-3011. |
| [19] | Chevrot A, Vernotte A, Legeard B. CAE: contextual auto-encoder for multivariate time-series anomaly detection in air transportation [J]. Computers and Security, 2022, 116: No.102652. |
| [20] | Fried A, Last M. Facing airborne attacks on ADS-B data with autoencoders [J]. Computers and Security, 2021, 109: No.102405. |
| [21] | Luo P, Wang B, Li T, et al. ADS-B anomaly data detection model based on VAE-SVDD [J]. Computers and Security, 2021, 104: No.102213. |
| [22] | 丁建立,张琪琪,王静,等. 基于Transformer-VAE的ADS-B异常检测方法 [J]. 系统工程与电子技术, 2023, 45(11): 3680-3689. |
| Ding Jianli, Zhang Qiqi, Wang Jing, et al. ADS-B anomaly detection method based on Transformer-VAE[J]. Systems Engineering and Electronics, 2023, 45(11): 3680-3689. | |
| [23] | Chen L C, Zhu Y, Papandreou G, et al. Encoder-decoder with atrous separable convolution for semantic image segmentation[C]// ECCV 2018, LNCS 11211. Cham: Springer, 2018: 833-851. |
| [24] | Xu G, Liao W, Zhang X, et al. Haar wavelet downsampling: a simple but effective downsampling module for semantic segmentation [J]. Pattern Recognition, 2023, 143: No.109819. |
| [25] | He K, Zhang X, Ren S, et al. Deep residual learning for image recognition [C]// CVPR 2016. Piscataway: IEEE, 2016: 770-778. |
| [26] | Yang L, Zhang R Y, Li L, et al. SimAM: a simple, parameter-free attention module for convolutional neural networks [J]. Proceedings of Machine Learning Research, 2021, 139: 11863-11874. |
| [27] | Woo S, Park J, Lee J Y, et al. CBAM: convolutional block attention module [C]// ECCV 2018, LNCS 11211. Cham: Springer, 2018: 3-19. |
| [28] | Network OpenSky. OpenSky Network homepage [EB/OL]. [2025-04-10].. |
| [29] | Ronneberger O, Fischer P, Brox T. U-net: convolutional networks for biomedical image segmentation [C]// MICCAI 2015, LNCS 9351. Cham: Springer, 2015: 234-241. |
| [30] | Xie E, Wang W, Yu Z, et al. SegFormer: simple and efficient design for semantic segmentation with Transformers [C]// NeurIPS 2021. Red Hook: Curran Associates Inc., 2021: 12077-12090. |
| [31] | Zhang W, Pang J, Chen K, et al. K-Net: towards unified image segmentation [C]// NeurIPS 2021. Red Hook: Curran Associates Inc., 2021: 10326-10338. |
| [32] | Poudel R P K, Liwicki S, Cipolla R. Fast-SCNN: fast semantic segmentation network[PP/OL]. arXiv (2019-02-12) [2025-04-10].. |
| [33] | Wang Q, Wu B, Zhu P, et al. ECA-Net: efficient channel attention for deep convolutional neural networks [C]// CVPR 2020. Piscataway: IEEE, 2020: 11531-11539. |
| [34] | Guo M H, Liu Z N, Mu T J, et al. Beyond self-attention: external attention using two linear layers for visual tasks [J]. IEEE Transactions on Pattern Analysis and Machine Intelligence, 2023, 45(5): 5436-5447. |
| [1] | Yifan WANG, Hu HAN, Dong LI, Yating FAN, Lin LI. Heterogeneous enhancement and multi-source knowledge fusion for aspect-based sentiment analysis [J]. Journal of Computer Applications, 2026, 46(9): 2752-2760. |
| [2] | Jielong BAI, Chenyun FANG, Zhiwei QIAO. Sparse CT artifact suppresion Transformer network based on multi-scale attention adaptive fusion [J]. Journal of Computer Applications, 2026, 46(8): 2660-2667. |
| [3] | Guanghui LI, Licheng QU. Dynamic dilated convolution and hierarchical local-global attention model based on improved Lite-Mono architecture [J]. Journal of Computer Applications, 2026, 46(8): 2567-2576. |
| [4] | Yuanhang HUANG, Na RONG. Model-free photovoltaic hosting capacity assessment method using attention mechanism and deep reinforcement learning [J]. Journal of Computer Applications, 2026, 46(8): 2708-2715. |
| [5] | Xiaojin GUO, Xuyang SUI, Kenan ZHOU. Channel estimation of STAR-RIS-assisted hybrid-field communication system based on deep learning [J]. Journal of Computer Applications, 2026, 46(8): 2548-2554. |
| [6] | Ming LIU, Dongqi SHEN, Ziyang MENG. Point cloud registration network with dual-branch multi-level feature fusion [J]. Journal of Computer Applications, 2026, 46(8): 2584-2593. |
| [7] | Fengchun LIU, Xinying SHAO, Chunying ZHANG, Liya WANG, Jing REN. FCMdepth: monocular depth estimation framework with multi-scale feature optimization [J]. Journal of Computer Applications, 2026, 46(8): 2603-2611. |
| [8] | Wei LIU, Weigang LI, Zhiqiang TIAN. Representation learning method of hierarchical rotation-invariant geometric structure for point cloud classification and segmentation [J]. Journal of Computer Applications, 2026, 46(8): 2594-2602. |
| [9] | Jianqiang YAN, Beibei DONG, Boting QU, Chen PENG. Bi-directional diffusion dynamic graph convolutional network with multi-source information fusion and graph-level attention for traffic flow prediction [J]. Journal of Computer Applications, 2026, 46(7): 2327-2333. |
| [10] | Xiuli DU, Xing GAO, Xiaoyu ZHANG, Chengsheng PAN, Qijie ZOU. Video snapshot compressive imaging reconstruction method based on dense spatio-temporal deformable attention [J]. Journal of Computer Applications, 2026, 46(7): 2288-2296. |
| [11] | Guoyou ZHANG, Hongyu NIE, Lihu PAN, Rundong LEI. Point-MLPBLS: point cloud semantic segmentation network based on MLP cascaded broad learning system [J]. Journal of Computer Applications, 2026, 46(7): 2259-2266. |
| [12] | Wenling LIU, Yong LI, Jiahui LI, Houkang ZHANG. Unsupervised dehazing method for remote sensing images with non-uniform haze [J]. Journal of Computer Applications, 2026, 46(7): 2297-2306. |
| [13] | Yasong ZHANG, Bihui CONG, Shuang XU. Graph neural network node classification model incorporating clustering coefficients [J]. Journal of Computer Applications, 2026, 46(6): 1855-1862. |
| [14] | Jun QIN, Xintao JIAO, Biqing ZENG. Non-intrusive load monitoring method combining BiLSTM-Transformer and Kolmogorov-Arnold network [J]. Journal of Computer Applications, 2026, 46(6): 2026-2033. |
| [15] | Jinxiao ZHANG, Chenglong LI, Xinyan GAO, Ming ZHANG. 3D human pose estimation model based on temporal-spatial feature pyramid network and multi-hypothesis interaction mechanism [J]. Journal of Computer Applications, 2026, 46(6): 1965-1972. |
| Viewed | ||||||
|
Full text |
|
|||||
|
Abstract |
|
|||||
