《计算机应用》唯一官方网站 ›› 2026, Vol. 46 ›› Issue (10): 3288-3297.DOI: 10.11772/j.issn.1001-9081.2025091078

• 计算机软件技术 • 上一篇    

基于大语言模型的多策略编译器模糊测试系统

李东辉1, 李颖颖2, 张春艳1, 刘鹏3()   

  1. 1.信息工程大学 网络空间安全学院,郑州 450001
    2.国家并行计算机工程技术研究中心,江苏 无锡 214083
    3.紫金山实验室 内生安全中心,南京 211000
  • 收稿日期:2025-09-19 修回日期:2025-11-10 接受日期:2025-11-12 发布日期:2025-12-18 出版日期:2026-10-10
  • 通讯作者: 刘鹏
  • 作者简介:李东辉(2001—),男,河南三门峡人,硕士研究生,CCF会员,主要研究方向:模糊测试、多面体编译优化、大语言模型
    李颖颖(1984—),女,河南开封人,副教授,博士,CCF会员,主要研究方向:模糊测试、编译器优化、先进编译
    张春艳(1990—),女,河南郑州人,讲师,博士,主要研究方向:人工智能、模糊测试、高性能计算
  • 基金资助:
    河南省自然科学基金资助项目(252300420988);先进计算与智能工程实验室基金资助项目(1017406)

Multi-strategy compiler fuzzing system based on large language models

Donghui LI1, Yingying LI2, Chunyan ZHANG1, Peng LIU3()   

  1. 1.School of Cyberspace Security,Information Engineering University,Zhengzhou Henan 450001,China
    2.National Research Center for Parallel Computer Engineering and Technology,Wuxi Jiangsu 214083,China
    3.Endogenous Safety and Security Center,Purple Mountain Laboratories,Nanjing Jiangsu 211000,China
  • Received:2025-09-19 Revised:2025-11-10 Accepted:2025-11-12 Online:2025-12-18 Published:2026-10-10
  • Contact: Peng LIU
  • About author:LI Donghui, born in 2001, M. S. candidate. His research interests include fuzzing, polyhedral compilation optimization, large language models.
    LI Yingying, born in 1984, Ph. D., associate professor. Her research interests include fuzzing, compiler optimization, advanced compilation.
    ZHANG Chunyan, born in 1990, Ph. D., lecturer. Her research interests include artificial intelligence, fuzzing, high-performance computing.
  • Supported by:
    Natural Science Foundation of Henan Province(252300420988);Open Fund of Advanced Computing and Intelligent Engineering Laboratory(1017406)

摘要:

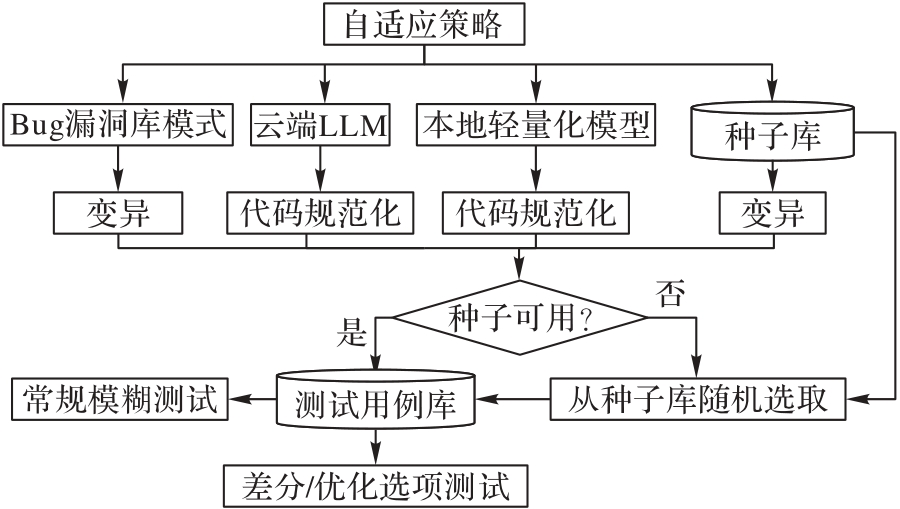
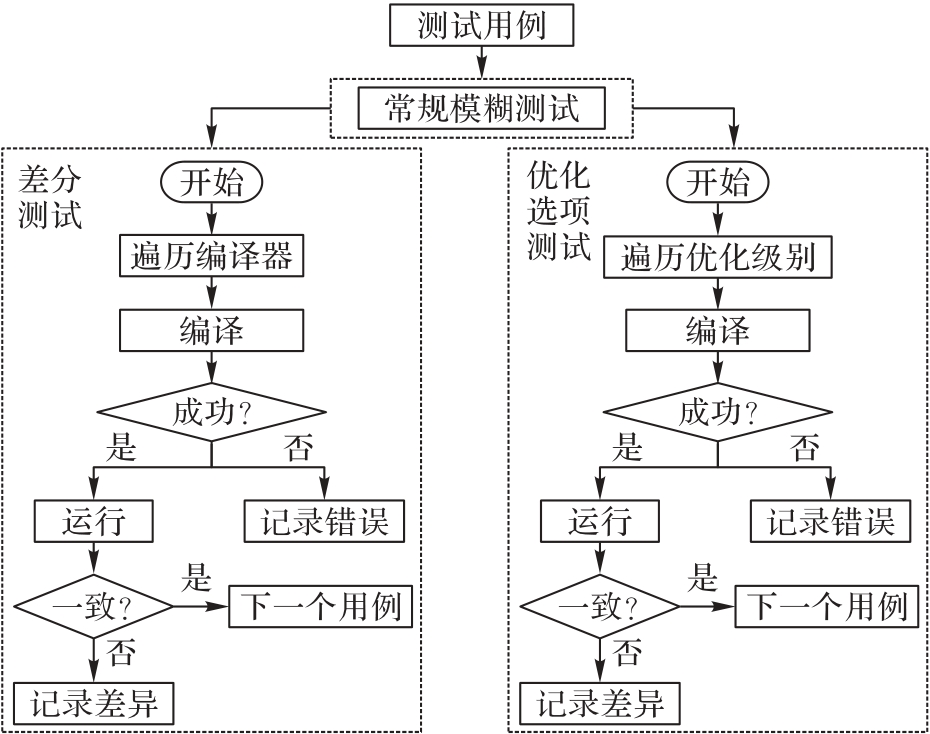
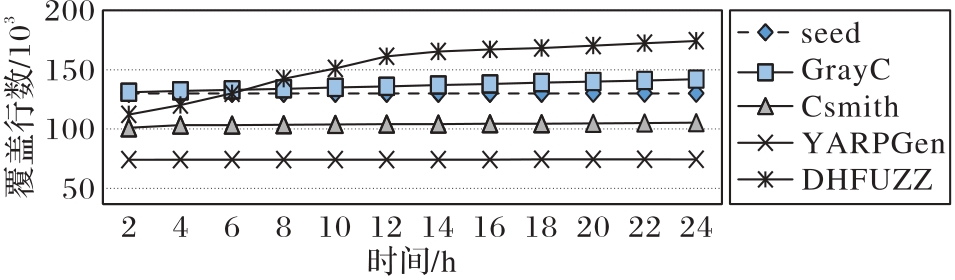
针对现有编译器模糊测试中普遍存在的测试用例多样性不足、测试成本高以及人工依赖性强等问题,提出一种基于大语言模型(LLM)的多策略编译器模糊测试系统——DHFUZZ(Deep & Hybrid FUZZer)。该系统融合多策略测试用例生成与LLM,通过调整提示词引导LLM生成多样化测试用例,并结合自定义代码生成器快速构造具备特定功能的测试代码。此外,该系统集成变异策略以进一步丰富测试用例,提升代码覆盖率,从而更有效地探索编译器潜在路径以触发深层漏洞。并且,系统设计端到端的自动化测试流程,以实现从测试用例生成、编译器执行到漏洞检测的全流程自动化。实验结果表明,DHFUZZ能够生成覆盖多种语法结构与语义特征的测试用例,在GCC(GNU Compiler Collection)、Clang等主流编译器测试中显著提高了代码覆盖率,展现出DHFUZZ的漏洞检测潜力,为编译器可靠性保障提供了一种高效、低成本的自动化测试方案。

关键词: 编译器测试, 模糊测试, 大语言模型, 测试用例生成, 差分测试

Abstract:

To address the common issues in the existing compiler fuzzing, such as insufficient test case diversity, high testing costs, and heavy reliance on manual intervention, a multi-strategy compiler fuzzing system based on Large Language Models (LLMs), DHFUZZ (Deep & Hybrid FUZZer), was proposed. In the system, multi-strategy test case generation was integrated with LLMs, thereby adjusting prompts to guide the LLM in generating diverse test cases, and the custom code generators were combined to construct test code with specific functions rapidly. Additionally, mutation strategies were incorporated to further enhance test case diversity and improve code coverage, thereby exploring potential compiler execution paths more effectively, so as to trigger deep vulnerabilities. At the same time, an end-to-end automated testing process was designed to fully automate the process from test case generation and compiler execution to bug detection. Experimental results demonstrate that DHFUZZ can generate test cases covering diverse syntactic structures and semantic features, and improves code coverage significantly in tests on mainstream compilers such as GCC (GNU Compiler Collection) and Clang, demonstrating its vulnerability detection potential, and providing an efficient and low-cost automated testing solution for compiler reliability assurance.

Key words: compiler testing, fuzzing, Large Language Model (LLM), test case generation, differential testing

中图分类号: